Our website is a professional certification dumps leader that provides GIAC GSLC exam dumps material and GSLC pass guide for achieving, not an easy way, but a smart way to achieve certification success in GSLC real exam. We are equipped with professionals having vast experience in the GSLC practice test; they are a committed team of individuals that make sure that the customers get the latest GSLC test questions and GSLC test answers. Our website is the single best training online tools to find your GSLC practice test and to study for your GIAC Security Leadership Certification (GSLC) real exam. Our aim is always to provide best quality practice exam products with best customer service.

How to Prepare For GSLC Certification Exam
Preparation Guide for GSLC Certification Exam
GSLC: Tips to survive if you don't have time to read all the page
The certification course for certified safety managers without suppliers has been designed for intermediate and senior managers, as well as for all engineers who wish to increase their knowledge in the field of security. Course C) SLO was designed to provide management with an essential understanding of current security issues, best practices, and technology. Because a manager or security officer understands the value of a security, he is ready to manage the security component of an IT security project. An SLO candidate can be seen as the bridge between cybersecurity equipment and operations, as well as business management. Encryption concepts and applications for managers, network concepts and monitoring for managers Management of a security operations center, application security, negotiations and structure of suppliers and programs. Security architecture, security awareness, security policy, and system security management Risk and security management framework, vulnerability management, incident response, and business continuity The candidate will demonstrate an understanding of the use of symmetric, asymmetric and hash algorithms to protect data in transit or at rest, as well as the importance of PKI and key management candidate will demonstrate his knowledge of current cryptographic terminology and his understanding of how symmetric, asymmetric and hash cryptography works The candidate will demonstrate that he understands the phases of accident response and the business continuity process.
The candidate will demonstrate an understanding of the main threats to the application code and software infrastructure, as well as the integration of security into the life cycle of software development and DevOps processes
About our products
Our website provides our customers with best GSLC pass collection study materials. Our GSLC exam dumps are written by IT experts who have vast experience and knowledge in the GIAC Security Leadership Certification (GSLC). The certified experts make sure that the GIAC GSLC exam cram is updated on a regular basis with GSLC real exam so every customer can prepare GSLC pass guide smoothly. The GSLC practice test will enable you to improve your ability with minimum time spent on GSLC real exam and maximum knowledge gained.
No Help, Full Refund
If you failed GIAC GSLC real exam with our GSLC pass guide, first you can choose to wait the updating of GSLC exam dumps or free change to other dumps if you have other test. If you want to full refund, please within 7 days after exam transcripts come out, and then scanning the transcripts, add it to the emails as attachments and sent to us. After confirmation, we will refund immediately.
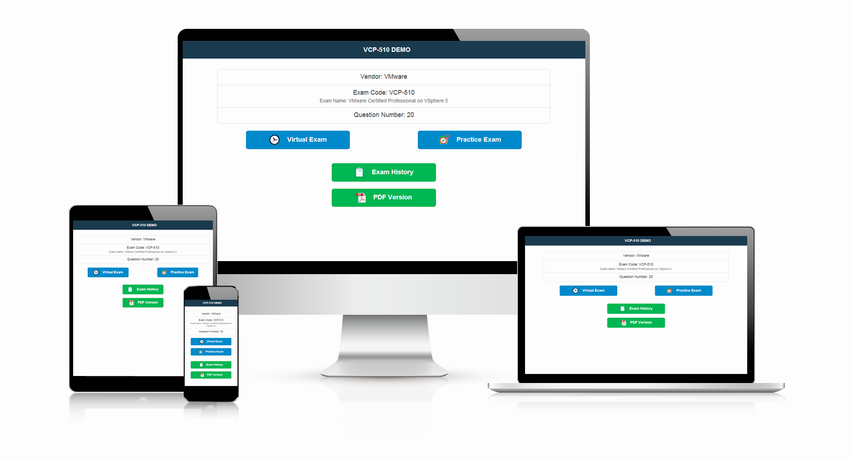
Difference between test engine and online test engine
Test engine and online test engine both are a simulation of actual test; you can feel the atmosphere of GSLC real exam by test engine and online version. You can only use test engine on the Windows operating system, but online version supports Windows/Mac/Android/iOS operating systems that mean you can practice GIAC GSLC test questions or test yourself on any electronic equipment. It doesn't limit the number of installed computers or other equipment.
GSLC Certification Path
There are no prerequisites for GSLC exam.
One-year free update
If you bought GSLC practice test study materials from our website, you will be allowed to free update your exam dumps one-year. If the latest version of GIAC GSLC exam dumps released, we will send it your email immediately, you just need to check your email.
24/7 customer assisting
We offer 24/7 customer assisting to support you in case you may encounter some problems, such as downloading or purchasing. If you have any problems please feel free to contact us.
Instant Download GIAC GSLC Exam Braindumps: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
Key Exam Facts
GIAC GSLC is an online proctored exam with a maximum time limit of 3 hours. It brings a total of 115 questions and has a minimum passing score of 65%. However, note that GIAC has all the rights to change the exam specifications without giving prior notice to students. So, it's always advisable to keep an eye on the GIAC official website to find out the latest information about the test before you register for it.
Considering quite an extensive set of topics to learn for the GSLC exam, it’s highly recommended to start your preparation early and use only credible materials. The vendor itself suggests applicants allocating about 4 months or 55 hours to get fully ready for this challenge. Below are some of the options to use for training and revision.
Reference: http://www.giac.org/certification/security-leadership-gslc
GIAC GSLC Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Cryptography Concepts for Managers | 6% | - Symmetric, asymmetric, and hashing basics - Cryptography governance - Cryptographic control selection and use |
| Managing System Security | 8% | - Endpoint security and protection strategies - System hardening and configuration management - Malware and attack types |
| Incident Response and Business Continuity | 10% | - Incident response lifecycle and management - Crisis management and communication - Business continuity and disaster recovery planning |
| Managing Security Policy | 10% | - Aligning policies with risk appetite - Policy, standard, guideline development - Policy implementation and enforcement |
| Managing the Program Structure | 12% | - Organizational culture and reporting structures - Security program design and governance - Personnel management and team leadership |
| Managing Negotiations and Vendors | 2% | - Contract and security requirements - Third-party risk management |
| Managing Application Security | 7% | - Application security risk management - DevOps and infrastructure security - Secure software development lifecycle |
| Risk Management and Security Frameworks | 12% | - Compliance and regulatory requirements - Risk assessment and mitigation strategies - Security frameworks (NIST, ISO 27001, CIS Controls) |
| Managing Security Awareness | 2% | - Awareness program design and delivery - Behavioral change and measurement |
| Managing a Security Operations Center | 6% | - Team and process management - SOC performance measurement - SOC structure and operations |
| Vulnerability Management | 4% | - Program management and reporting - Vulnerability assessment and remediation |
| Network Monitoring for Managers | 7% | - SIEM and alert management - Centralized logging and monitoring strategies - Monitoring program oversight |
| Managing Projects | 2% | - Resource and timeline planning - Security project management |
| Network Security Architecture | 8% | - Network security controls - Secure network design - Security architecture and trust models |
| Networking Concepts for Managers | 8% | - Network defense principles - Core network protocols and technologies - Common network threats and vulnerabilities |
GIAC Security Leadership Certification (GSLC) Sample Questions:
You are responsible for security at a company that specializes in e-commerce. You realize that given the high volume of Web traffic, there is a significant chance of someone being able to breach your perimeter. You want to make sure that should this occur, you can redirect the attacker away from sensitive data. How would you best accomplish this?
- A. Implement a stateful packet inspection firewall.
- B. Implement a honey pot.
- C. Implement a passive IDS
- D. Implement a network based IDS.
Correct Answer: B 🗳️
According to Microsoft's privacy guidelines, which of the following data types includes statistic from aggregate information?
- A. Pseudonymous Data
- B. Sensitive Personally Identifiable Information
- C. Personally Identifiable Information
- D. Anonymous Data
Correct Answer: D 🗳️
Which Temporal Metric does the Common Vulnerability Scoring System (CVSS) use to indicate if a temporary fix is available for a vulnerability?
- A. Report Confidence
- B. Integrity Impact
- C. Remediation Level
- D. Exploit Code Maturity
Correct Answer: C 🗳️
Which of the following terms describes the statement given below?
"It refers to a range of skills, tools, and techniques used to manage
time when accomplishing specific tasks, projects, and goals. This set
encompasses a wide scope of activities, and these include planning,
allocating, setting goals, delegation, analysis of time spent,
monitoring, organizing, scheduling, and prioritizing."
- A. Perception Management
- B. Change Management
- C. Time Management
- D. Digital Rights Management
Correct Answer: C 🗳️
Which of the following documents is described in the statement below?
"It is developed along with all processes of the risk management. It contains the results of the qualitative risk analysis, quantitative risk analysis, and risk response planning."
- A. Risk register
- B. Risk management plan
- C. Project charter
- D. Quality management plan
Correct Answer: A 🗳️
Viewing page 1 out of 134 pages.
Viewing questions 1-5 out of 667 questions.


 Doris

 George

 Leonard

 Barton
 Gilbert
 Noel
 Emma
 Drew
 Fanny
 Eleanore
 Julie
 Ivy
 Dana
 Kent
 Lindsay
 Tracy
 Barry
 Hyman
 Maurice
 Dunn
 Lucy
 Josephine